SaaS product for SOC 2 readiness & AI governance
Know exactly what you are missing.
TROS takes in your evidence, maps it to controls, reviews every item, and tells you what is missing and why. SOC 2 readiness and AI governance run on the same engine.
Run the AI readiness assessment yourself, no account required. Walkthroughs are run live, on a working system.
Security reviews don't fail because teams lack policies. They fail because teams can't prove what they have.
Nothing counts until a reviewer confirms it, so the number on your dashboard is one you can defend in the room.
What review looks like
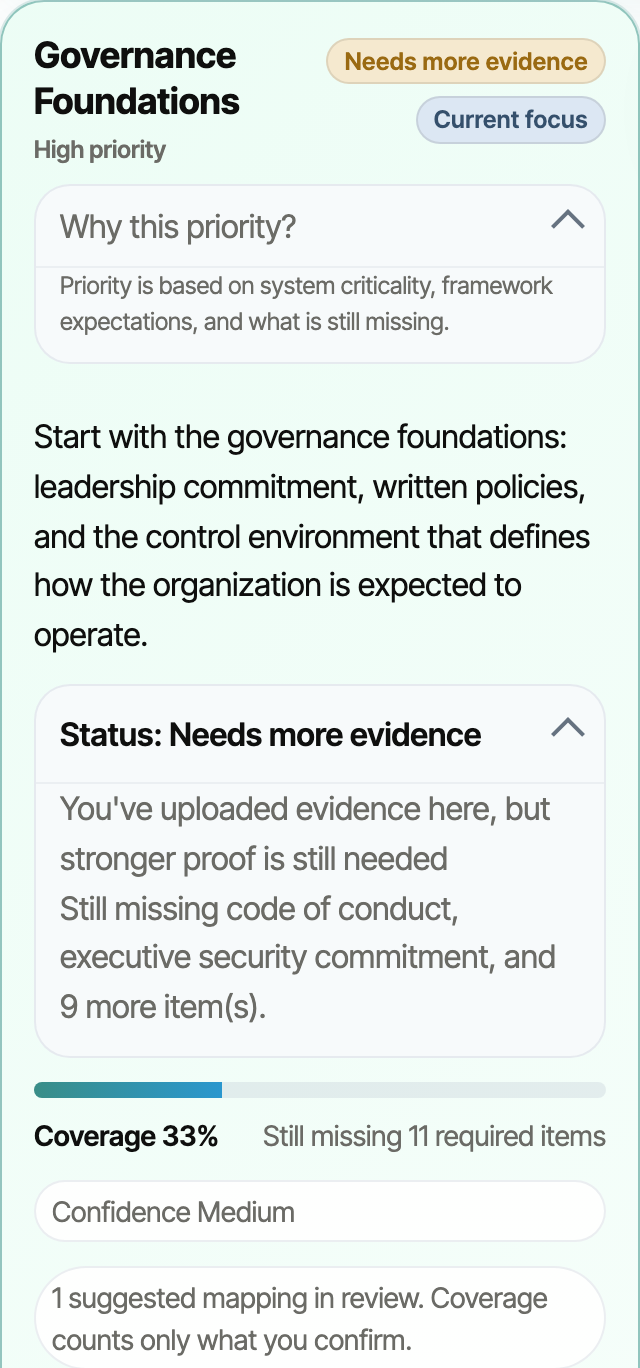
Every evidence area carries a status, a coverage figure, a count of what is still outstanding, and the reason it sits where it does. The coverage number moves only when a reviewer confirms an item, which is why the product says so on the card itself.
What it does
Four jobs that usually disappear into spreadsheets, shared drives, and email threads.
Takes evidence in the form you already have it
Policies, exports, screenshots, tickets, meeting records. TROS reads what you upload and figures out which controls it speaks to, so the sorting is not your job.
Maps evidence to established control frameworks
Evidence is mapped to the applicable SOC 2 Trust Services Criteria, and TROS identifies where it is sufficient, incomplete, or missing. The AI readiness track runs its own question set, authored against NIST AI RMF, ISO 42001 and the EU AI Act.
Reviews each item and says why
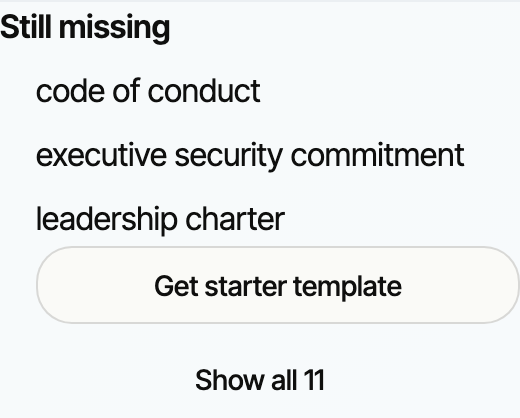
Every piece of evidence gets a verdict, a confidence level, and a next step. Gaps are named as the missing artifact, not as a percentage that went down.
Runs the review loop
Managers review, contributors respond, disputes are tracked to a decision. The record of who confirmed what, and when, is the thing you hand to the auditor.
Two tracks
One evidence engine, two of the things enterprises ask you to prove.
SOC 2 readiness
Evidence mapped to the Trust Services Criteria, a verdict on each item, and a gap list naming the artifacts you still need. Built for the security review sitting between you and a signed enterprise contract. TROS supports readiness and evidence review. It does not replace the independent CPA firm that performs a SOC 2 examination.
AI readiness
A tiered assessment of how your AI systems are governed, with each question authored against the NIST AI Risk Management Framework, ISO 42001 and the EU AI Act. Drafted from your own evidence, confirmed by an authorized reviewer before it is shared.
Open to run cold. Create an account afterward if you want to keep the result.
Control sets and frameworks in the platform
SOC 2 is the framework TROS assesses your evidence against. The AI governance frameworks are referenced by the AI readiness question set. None are certifications held by TROS, and an assessment is not an audit opinion.
How your evidence is handled
You decide how far your evidence travels.
What a model receives
Masked before it leaves
No text reaches a third-party model unmasked. Names, emails and other identifying details are replaced with tokens first, and you can add terms of your own.
Or it does not leave at all
Evidence can be evaluated by a model running inside your own instance, with no external model provider anywhere in the path.
On infrastructure you can name
Firms and regulated buyers can run TROS on dedicated infrastructure rather than shared, available as a deployment option on the plan. Full data handling detail, channel by channel, is documented for your security review.
Who it is for
Built for growing companies facing enterprise scrutiny.
TROS helps small security, technology and compliance teams prepare for SOC 2 reviews, customer security assessments, and AI governance questions, without running the work through spreadsheets and shared drives.
A deal is contingent on SOC 2, or the security questionnaire has arrived, or a customer wants to know how your AI is governed before they sign. You have no compliance team to put on it, and the established platforms are priced for companies several stages ahead of you.
Second deployment model
Advisory and readiness firms managing multiple client engagements run TROS as their own tenant, with each client engagement kept separate. Firm branding and your own control language are what we are building next, with our first partner firms.